

TL;DR
Pulse Security AI’s 42-person survey found 71% spent 10+ hours preparing each board cycle while 55% said their board had no formally defined cyber risk appetite.
NACD’s 2026 guidance says the board and management should define that appetite, then report current exposure against it.
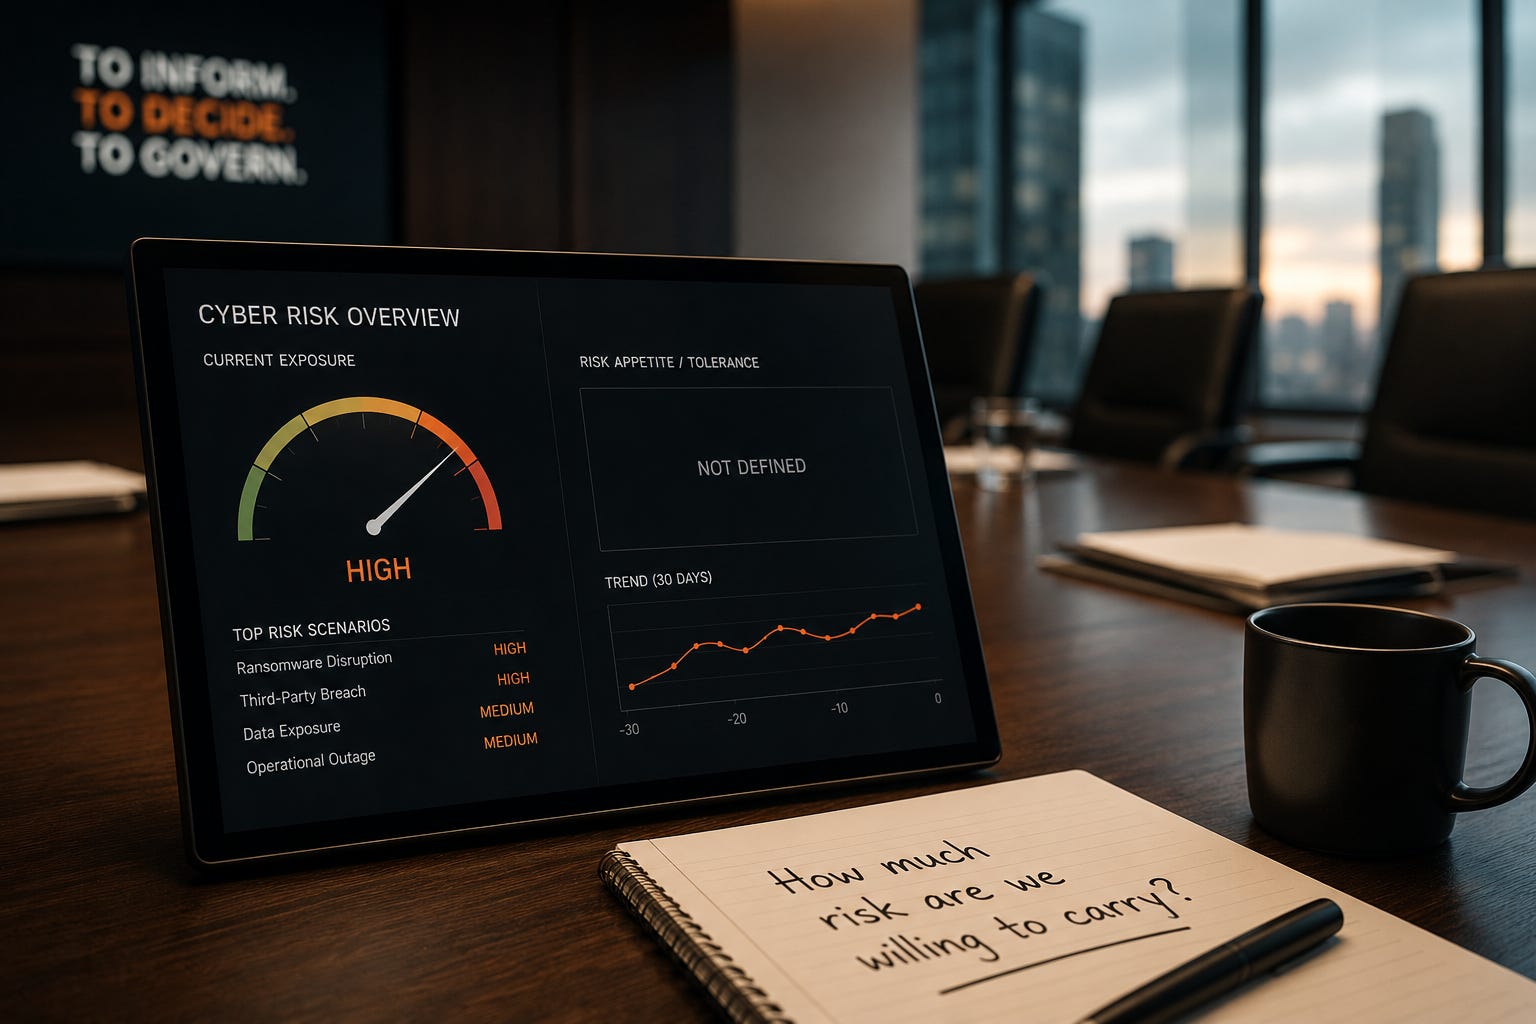
Better slides can’t replace the missing decision about how much risk the company is willing to carry.
Pulse Security AI surveyed 42 security leaders and corporate directors about board reporting.
Seventy-one percent said they spend at least ten hours preparing for each board cycle. Fifty-five percent said the board has never formally defined the company’s cyber risk appetite.
Those two numbers don’t belong in separate conversations.
The first says security teams spend a lot of time building the report. The second says many of those reports have no agreed threshold to report against.
The usual advice is better storytelling. Shorten the deck. Replace CVSS scores with business scenarios. Add financial exposure. Put the architecture diagram in the appendix.
And that’s all useful.
But eventually somebody has to answer a different question: How much of this risk are we willing to carry?
If nobody has answered it, the CISO can spend two days polishing the presentation and still walk into the room without the one thing that makes the colors mean anything.
Ten Hours Against No Baseline
The Pulse numbers need the usual vendor-survey caveat.
Pulse is a security-program-management company. Its survey had 42 respondents, 70% of them CISOs or heads of security, plus more than 20 in-depth interviews and two workshops involving roughly 22 CISOs. Pulse says directly that the statistics aren’t nationally representative.
So I wouldn’t turn 55% into an estimate of every corporate board in America.
I‘d treat it as a field signal.
Especially because the 2026 NACD and Internet Security Alliance Director’s Handbook on Cyber-Risk Oversight describes exactly the governance step the survey says is often missing.
NACD’s Principle Four says the board should work with management to define the organization’s cyber-risk appetite: the amount and types of risk it is willing to accept while pursuing its objectives. NACD says that appetite should be explicit, quantitative where possible and expressed in business or financial terms. Management then operates the program inside that direction.
Principle Five completes the loop. NACD says board reporting should show current exposure against the board-approved risk appetite.
First define the boundary. Then report where you are relative to it.
That’s a different job from making a technical dashboard easier to understand.
Red and Green Need a Reference Point
A critical vulnerability can be technically severe whether your board likes it or not. Severity and business acceptance are different questions.
The board isn’t there to decide whether CVSS 9.8 is a large number. It needs enough information to understand what the scenario can do to the business, how exposed the company is and whether management is operating inside the risk boundary the company agreed to.
That last part disappears when the appetite was never defined.
Imagine two identical red boxes on two board dashboards.
At Company A, red means estimated exposure exceeds a board-approved threshold and management needs a decision on treatment.
At Company B, red means the security team thinks the situation is bad.
Same color. Different governance.
Company A encoded a prior decision into the report. Company B encoded an opinion.
This is where I think we sometimes give CISOs the wrong communication advice. We tell them to stop speaking security and start speaking business. Fine. But business language doesn’t create a business decision nobody made.
Pulse found another version of this in its small sample. Forty-nine percent primarily described cyber-risk severity with qualitative categories. Only 3% primarily used quantified dollar amounts.
I wouldn’t turn that into “everything needs a dollar sign.” Fake precision is not maturity. NACD itself says quantitative where possible. A qualitative boundary can still be a boundary.
The failure is having none.
“Speak Business” Is Downstream Advice
Take ransomware against a critical operation.
A CISO can explain the likely interruption, which services are exposed, what recovery looks like, which controls are missing and the plausible financial consequences.
The board may understand every word.
There‘s still another decision: is that exposure acceptable?
Maybe the company is willing to carry more risk because reducing it would delay a major launch. Maybe the potential loss sits outside anything the company wants to tolerate. Maybe management should transfer part of it through insurance, spend to reduce it or explicitly accept it for six months.
Security can model those choices and recommend one. Security shouldn’t quietly make the enterprise risk decision by deciding whether a box is red.
NIST IR 8286A Rev. 1 comes at the same problem from the enterprise-risk side. The December 2025 revision describes cybersecurity risk analysis in the context of risk appetite and risk tolerance, then uses risk registers to help decision-makers prioritize risk response and monitoring.
So the threshold is not decoration around the risk analysis. It It’s an input to it.
If the company never established that input, the CISO ends up reverse-engineering risk appetite from whatever gets approved, delayed or funded.
You find out what the company was supposedly willing to risk only after somebody reacts to the recommendation.
That’s backwards.
The Board Meeting Should Produce a Decision
Pulse reported one number I think deserves more attention than it got: half of respondents said their boards had made no explicit decision to accept, mitigate or transfer cyber risk during the prior year.
Again, small sample.
Still worth asking about your own board.
If a quarterly cyber meeting produces questions, discussion and another request for slides but never an explicit risk decision, what exactly is the meeting governing?
My read is that a lot of organizations have turned the cyber board deck into a briefing instrument. The CISO explains the environment. Directors ask questions. Everybody leaves better informed.
NACD’s model asks more of the meeting.
The report should show where current exposure sits relative to a boundary the board already approved. When exposure crosses that boundary, management reduces it, transfers it, avoids it or comes back with a reason the company should accept more.
That changes the package.
For each material scenario, I’d want five things: the scenario, current exposure, the agreed appetite or tolerance, management’s recommended response and the decision required from the board.
Examples: ransomware disrupting a core operation, compromise of sensitive customer data, failure of a critical third party.
Then stop.
The vulnerability inventory can live somewhere else.
And if the company has never defined the appetite, don’t hide that absence behind a heat map. Put it on the agenda.
The Missing Decision
Only 12.5% of the security leaders in Pulse’s survey said they were very confident that the board walked away from a presentation understanding the true state of the security program.
The obvious response is another round of communication training.
Maybe some CISOs need it.
But communication isn’t always the first failure.
A board report can explain the security posture clearly and still leave directors unable to judge whether the posture is acceptable. That happens when reporting gets built before risk appetite does.
So before spending another ten hours on the deck, look at the red, yellow and green boxes and ask what each one is measured against.
If the answer is a board-approved risk boundary, good. Improve the report.
If the answer is “we haven’t actually set one,” stop polishing slide four.
That’s the first item on the agenda.
Resources
Pulse Security AI, The CISO-Board Communication Gap, August 2026. Survey of 42 security leaders and corporate directors, 20+ interviews and two moderated workshops with roughly 22 CISOs. Pulse explicitly states that the statistics are not nationally representative.
National Association of Corporate Directors and Internet Security Alliance, 2026 Director’s Handbook on Cyber-Risk Oversight, Principle Four: Adopt an Enterprise Framework for Managing Cyber Risk, April 16, 2026.
National Association of Corporate Directors and Internet Security Alliance, Principle Five: Guide Cybersecurity Risk Measurement and Reporting, April 16, 2026.
NIST IR 8286A Rev. 1, Identifying and Estimating Cybersecurity Risk for Enterprise Risk Management, December 2025.
Analytical note: the argument that an undefined risk appetite can make otherwise accurate board reporting less decision-useful is my interpretation of the governance guidance and survey findings above. Pulse’s sample is small and non-representative.